
ESG Reporting
What Does Sustainability Assurance Actually Tell You?
“The report has been assured, so the information must have been checked.”
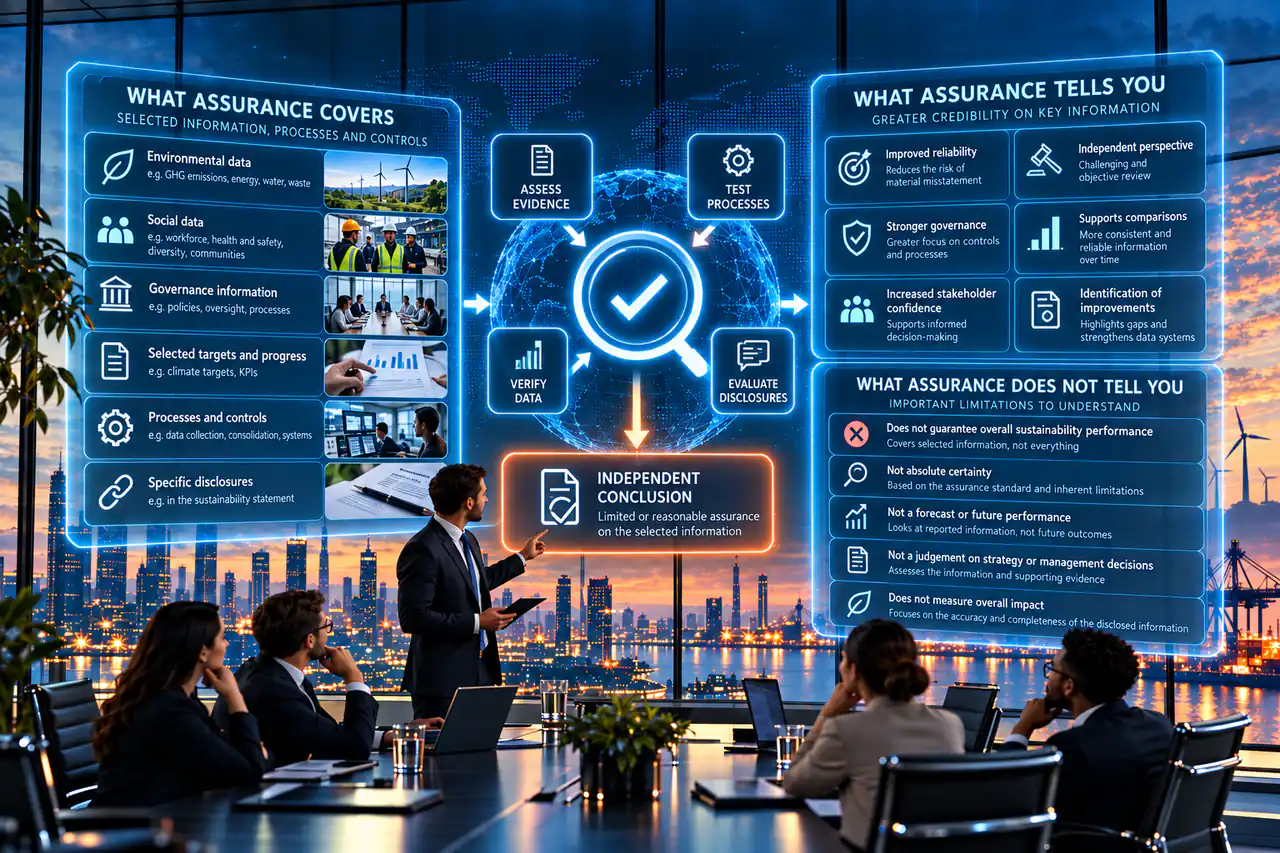
It is a natural assumption. It is also partly correct. An assurance provider has performed procedures, obtained evidence and reached a conclusion the reader can rely on. What that conclusion covers is a narrower question than the word “assured” suggests.
The more useful question is what exactly was assured: which information, against what criteria, within what scope and to what level of assurance. The answer determines what the conclusion tells the reader. Our previous article looked at when assurance happens in the reporting process. This one looks at what it establishes.
An assurance engagement is not a line-by-line examination of every record an organisation holds. Under ISSA 5000, the international standard the Securities Commission has designated for Malaysia, the assurance provider obtains sufficient appropriate evidence about the information within the scope of the engagement and expresses a conclusion on it. That is the nature of assurance rather than a weakness in it.
An assurance provider can test the information within the agreed scope. That is not necessarily the same as establishing that every relevant piece of information has been identified.
A reported number and the population behind it
Consider a large organisation with a head office and regional offices, hundreds of smaller operational locations, data centres, network infrastructure, customer-facing branches, leased premises and sites run by agents, franchisees or outsourced providers. Its electricity consumption feeds its Scope 2 emissions, which the largest Malaysian listed issuers will need to have reasonably assured from 2028.
The reporting team compiles an electricity dataset. The assurance provider may examine a selection of bills, reconcile the dataset to accounting records, recalculate the emissions, investigate unusual movements and trace reported figures to supporting evidence. Each of those procedures tests the information in the dataset.
A different question sits underneath: how do we know the dataset contains every relevant operation and location? A site that never entered the dataset generates no bill to sample, no anomaly to investigate and no figure to trace.
Population and Evidence
What Testing Can and Cannot Reach
An organisation’s sites
- Sampled. Bills examined, figures traced to evidence.
- In the dataset. Reconciled, recalculated, checked for anomalies.
- Never entered the dataset. No bill to sample, no anomaly to investigate, no figure to trace.
Reporting population
What should be included?
Completeness
Evidence
Is it supported?
Accuracy
Both: greater confidence
Testing answers the evidence question. The population question starts with what the organisation knows about itself.
Illustrative. Assurance procedures do consider the risk of omission; they work from the organisation’s own records of what exists.
ISSA 5000 does treat omission as a form of misstatement. Among the assertions it describes, completeness means that all events or conditions pertaining to the entity and its reporting boundary that should have been included have been included. Its own example is a company that reports rehabilitation work at three mining sites while saying nothing about two others. The assurance provider considers that risk and responds to it. Its procedures, however, work with the organisation’s own records, which start from what the organisation knows about itself.
Accuracy is not the same as completeness
Accuracy asks whether the information provided is correct and supported. Completeness asks whether the relevant population or information has been identified. The two can come apart in either direction. A third question, currency, adds another way for them to diverge.
Information can be accurate but incomplete: every figure in the dataset is right, but a relevant location or activity has been left out. It can be complete but inaccurate: every relevant site has been identified, but some readings were transcribed wrongly or an unsuitable emission factor was applied. It can be accurate and complete but outdated: it was once correct and once covered everything, but it no longer reflects current policies, operations or circumstances.
| Situation | Accurate | Complete | Current |
|---|---|---|---|
| What the reader may assume | |||
| Accurate but incomplete | × | ||
| Complete but inaccurate | × | ||
| Accurate and complete but outdated | × |
The reporting standards draw the same distinction. IFRS S1 asks that information faithfully represent what it purports to represent; to do so it should be complete, neutral and accurate. The GHG Protocol makes completeness one of its accounting principles: an inventory accounts for all emission sources and activities within the chosen boundary and discloses any specific exclusion. Adding the level of assurance gives four questions a reader can ask of any assured figure.
Four Dimensions of Confidence
Four Different Questions
Accuracy
Is the information provided correct and supported?
Completeness
Has the relevant population or information been identified?
Currency
Does the evidence still reflect the organisation, its activities and its current policies?
Assurance level
What procedures were performed and what level of confidence does the engagement provide?
Greater confidence
A strong answer to one question does not answer the others.
An explanatory model for this article, not a formal assurance framework.
How do you know the population is complete?
In a small organisation the question barely arises. In a large, decentralised one it is genuinely difficult. The group may have many legal entities, recent acquisitions and disposals, leased locations, outsourced activities, franchises, agents, temporary sites, changing suppliers and decentralised procurement. Operating arrangements change during the year.
The sustainability reporting team may not automatically know that a location has closed, a franchise agreement has ended or a new site has opened. It may not know that an outsourced facility has changed provider or that an activity is now managed by another entity in the group. That information usually exists somewhere: in property records, legal registers, procurement systems or operational management. It does not necessarily reach the people compiling the sustainability data.
Completeness is partly a reporting-boundary and management-information question, not simply a testing question.
ISSA 5000 reflects this. Before accepting an engagement, the assurance provider considers whether the entity has a process to identify the sustainability information to be reported; without one, the standard notes, it may be difficult to establish whether management has a reasonable basis for that information. At the end of the engagement, management confirms in writing that it has provided all relevant information and reflected all relevant matters in the sustainability information. Both steps place the starting point for completeness with the organisation. For an emissions inventory, that starting point is the organisational and operational boundary.
The same issue applies to qualitative information
Evidence is not only a question for numbers. Consider a familiar sentence: “The Group is committed to addressing climate change.” Where is the commitment documented? Is there a policy or strategy behind it and has that been approved? Does the current policy still support the statement? Is it describing a current commitment or a position the Group held some years ago?
Or take a statement that the Group conducted employee training. The supporting evidence might be training records, attendance lists, dates, the scope of the programme and information about participants. If the statement says “all relevant employees”, the evidence also needs to show who the relevant employees were; completeness again.
The issue is not whether a statement sounds reasonable. Most do. It is whether there is sufficient evidence to support it within the assurance scope. Narrative on governance, strategy and risk management is increasingly where readers look for judgement. The Advisory Committee on Sustainability Reporting’s 2025 consultation proposed bringing the IFRS S1 core content within reasonable assurance in later years; its decision on that proposal is still to come.
Information can become outdated
Evidence has a date. A report may state that the Group’s policy requires a particular practice when the policy has since been revised. It may state that the Group conducts an activity that has since ended. It may say that all relevant employees receive training when the programme has changed.
In each case the evidence may be genuine. The signed policy exists; the training records are real. They describe a position that has moved.
Evidence can be authentic and still no longer support the statement being made.
This is a particular process risk where narrative is carried forward from one year’s report to the next. Carrying text forward is efficient and often appropriate. The risk lies in carrying it forward without confirming that it still describes the organisation as it is. Currency asks whether the statement is still true for the period the report covers, not only whether evidence for it once existed.
How rigorous can assurance reasonably be?
It is tempting to think the answer is more testing. In principle an assurance provider could always test further. A large organisation may have hundreds of thousands of transactions, thousands of locations, many data sources, several systems and records held locally. Testing every item is rarely proportionate or necessary to reach the conclusion the engagement is designed to give.
At the same time, readers may reasonably assume that if something were wrong the assurance provider would have found it. Between those two positions sits a natural tension: depth of testing on one side; cost, time and practicality on the other.
ISSA 5000 is direct about it. Reducing engagement risk to zero is very rarely attainable or cost-beneficial, so even reasonable assurance is less than absolute. The reasons it gives include selective testing, the inherent limitations of internal control, evidence that is persuasive rather than conclusive and the use of professional judgement.
More testing does not automatically produce proportionately more confidence. Extensive testing of an incomplete population cannot establish that the omitted information does not exist.
Reasonable assurance and limited assurance
ISSA 5000 recognises two levels of assurance. In a reasonable assurance engagement the assurance provider reduces engagement risk to an acceptably low level and expresses an opinion; typically, that the information is prepared, in all material respects, in accordance with the applicable criteria. In a limited assurance engagement the acceptable level of risk is higher. The procedures are limited in nature, timing and extent compared with reasonable assurance. The conclusion states whether anything has come to the provider’s attention that causes it to believe the information is materially misstated.
Limited assurance is not acceptance without work. The standard requires the level of assurance obtained to be meaningful: likely to enhance users’ confidence to a degree that is clearly more than inconsequential. Reasonable assurance, for its part, is not certainty. A single engagement can also combine the two, with reasonable assurance over some information and limited assurance over the rest.
Neither level of assurance is a guarantee that every error or omission will be identified. The level affects the nature and extent of the procedures performed and therefore the degree of confidence that can reasonably be obtained.
Malaysia is moving towards reasonable assurance for emissions. The Securities Commission confirmed in September 2026 that reasonable assurance of Scope 1 and Scope 2 emissions under ISSA 5000 will apply to the largest Main Market issuers for periods beginning on or after 1 January 2028, with other issuers following. Until then, Bursa Malaysia’s Listing Requirements ask issuers to state whether the sustainability statement has been reviewed by internal auditors or independently assured. The assurance statement itself is where a reader learns which level applies and to what.
Assurance does not transfer responsibility for the data
ISSA 5000 engagements proceed on the basis that management acknowledges responsibility for preparing the sustainability information in accordance with the applicable criteria. Management is also responsible for the internal control needed to prepare it free from material misstatement; where appropriate, so are those charged with governance. The assurance provider is responsible for its own procedures and conclusion. It does not take over the records the conclusion rests on.
- Business and operationsCarry out the activities and hold the original records.
- Data ownersCompile and maintain particular datasets.
- Reporting teamBring the data together and prepare the disclosures.
- ManagementResponsible for the information and the controls behind it.
- Assurance providerResponsible for its procedures and its conclusion within the agreed scope.
- Board and usersOversee the information and rely on it.
Assurance does not transfer ownership of the underlying information from management to the assurance provider.
The same logic runs through the rest of the chain. An ESG consultant does not become the owner of operational data because it designed the template the data was collected in. A data owner responsible for electricity at one business unit does not necessarily know every activity across the group. The assurance provider does not become responsible for running the business or maintaining its records. Each role is necessary; none substitutes for clear ownership and review inside the organisation.
The question is not “Who is to blame?”
A missed activity, an outdated policy or an incorrect number may come to light through internal review, management review, assurance, the preparation of the next report, a stakeholder’s question, a later year’s calculation or an improved data system. How it was found matters less than what happens next.
The useful questions are practical. What happened and why was it missed? What information should have existed and where? What control or process could identify it earlier? Does the issue affect figures reported in previous years? What should change next year? The question about previous years connects to how restating GHG emissions works: a restated figure usually reflects better information rather than a past failure.
Sustainability reporting is not a once-a-year exam
Sustainability reporting is not a test in which the objective is to achieve a perfect score once a year. It is an information system that should become more reliable as the organisation learns from errors, gaps and changing circumstances.
Reporting systems mature, often in a recognisable pattern:
Year 1
A reporting boundary is established.
Year 2
An omitted activity is identified: leased sites whose electricity was paid by the landlord and recharged.
Year 3
The process changes so that new leases are captured when they are signed.
That sequence is improvement rather than failure. Errors should not simply be accepted: the second year’s discovery is only useful if the third year’s process changes. The measure of a reporting system is whether it learns.
What creates stronger confidence?
Confidence in sustainability information comes from several layers, each answering a different question. A clear boundary sets out which entities, operations and activities are included. Defined ownership establishes who is responsible for each dataset. Evidence supports the reported information; reconciliation connects reported figures to the underlying records. Current documentation shows that policies and procedures still reflect practice. Management review challenges the information before it is published. Independent assurance tests it within an agreed scope. Learning uses the findings to improve the process the following year.
The layers apply as much to judgements as to figures. A materiality assessment or a climate scenario analysis also has a boundary of what was considered, evidence behind its conclusions and a review it either did or did not receive.
Confidence Is Cumulative
Confidence Is Built in Layers
Defined boundary
Which entities, operations and activities are included?
Clear ownership
Who is responsible for each dataset?
Evidence
What supports the reported information?
Reconciliation
Can reported figures be connected to the underlying records?
Current documentation
Do policies and procedures still reflect practice?
Management review
Has management challenged the information?
Assurance
Has independent assurance been performed within an agreed scope?
Learning
Findings from every layer improve the boundary, ownership and evidence for the following year.
Confidence is built through layers rather than created by a single assurance statement. Assurance tests what the layers beneath it produce.
Illustrative. An explanatory model, not a formal assurance framework; organisations build these layers in different ways.
What an assurance statement should mean to the reader
An assurance statement repays careful reading. It sets out what information is covered and against which criteria; the level of assurance; the scope and boundary of the engagement; any limitations or inherent uncertainties; and the form and wording of the conclusion.
Read this way, the statement tells the reader a good deal. It says that an independent provider has performed procedures on defined information and reached a conclusion at a stated level. It does not say that every line of every underlying record has been independently checked. Assurance providers do not claim that it does.
Confidence is broader than the statement
Good assurance does not mean that every possible error or omission has been eliminated. It means that an appropriate level of independent work has been performed within a defined scope and against defined criteria.
Confidence in sustainability information is therefore broader than the assurance statement itself. It depends on clear boundaries, accountable data ownership, supporting evidence, appropriate review and a process that learns when gaps are identified. Assurance matters; so do the evidence, the completeness of the population and the people who own it. None of them removes uncertainty on its own.
The objective is not to create the illusion of perfect information. It is to build an information system that becomes more reliable, more transparent and more useful over time.
References
- IAASB, International Standard on Sustainability Assurance (ISSA) 5000, General Requirements for Sustainability Assurance Engagements, November 2024, on the definitions of reasonable and limited assurance, the preconditions for an engagement, management’s responsibilities and written representations, assertions including completeness and why reasonable assurance is less than absolute.
- Securities Commission Malaysia, ‘ACSR’s Mandatory Sustainability Assurance Requirement to Take Effect in 2028’, media release, 17 September 2026.
- Advisory Committee on Sustainability Reporting, Public Consultation Paper No. 2/2025: Proposed Framework for Sustainability Assurance, 2025.
- IFRS Foundation, IFRS S1 General Requirements for Disclosure of Sustainability-related Financial Information, 2023, on faithful representation.
- GHG Protocol, A Corporate Accounting and Reporting Standard, revised edition, on the completeness principle.
- Bursa Malaysia, Main Market Listing Requirements, Practice Note 9, on the statement of internal review or independent assurance.
Ace CSR supports Malaysian companies with GHG accounting, sustainability reporting and IFRS S1 and S2 advisory, including the reporting boundaries, data ownership and evidence that assured information rests on.
Explore More
Preparing sustainability information for assurance?